Patching Makes Me Drink

Empirical Security is inviting security pros to a virtual holiday wine tasting. You’ve survived another year of criticals, patch cycles, and “why isn’t this fixed yet?”. Now pour a glass with people who get it.

Sign Up

By submitting to this form, you accept the terms in our privacy policy.
A glass of red wine beside a laptop showing a video call of people raising wine glasses, with holiday lights behind

Event Details

Date: Wednesday, December 9, 2026

Time: 6:00 PM ET / 3:00 PM PT

Where: Virtual. You'll get a join link after you register.

Wine: Register by 11/23 to get your tasting kit shipped in time. [We can’t ship wine to Utah or Mississippi, and restrictions apply in some countries. Must be 21+.]

Meet our guest speaker
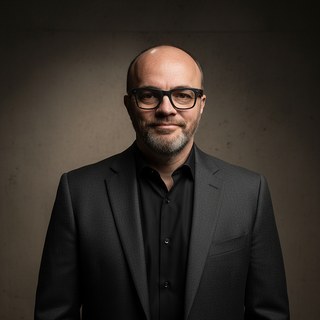
Jerry Gamblin

Jerry Gamblin is Head of Research at Empirical Security and the founder of RogoLabs, where he builds open tools like CVE.ICU and CVEForecast that turn public CVE data into something defenders can act on. He serves on the CVE Program’s Automation, Quality, and Consumer working groups, contributes to the FIRST EPSS Special Interest Group, and previously held senior research roles at Kenna Security and Cisco. Vulnerability management teams follow his work because he publishes the data and code behind his findings. Jerry will cover what he’s watching across the vulnerability landscape heading into 2027, then take your questions live. Nothing is off the table.

Why you should come

This year brought record CVE volume, shorter exploit windows, and more criticals than anyone could actually patch. For one evening you can stop triaging.

Join fellow threat and vulnerability management pros for a guided virtual wine tasting, a candid talk on the topics shaping our field, and a little holiday cheer. No slides about ticket SLAs. Just good wine and better conversation.

What to expect

• A guided tasting: 3 wines shipped to your door before the event.

• Jerry Gamblin’s Naughty and Nice Vulnerabilities: Jerry has checked his list twice. He’ll share which vulnerabilities earned a lump of coal this year and which ones turned out better than their scores suggested, and why.

• Live Q&A: Bring the questions you can’t ask in a change advisory board meeting.

• Peer conversation: Swap stories with people who live in the scanner and the ticket queue too.

FAQ

Who can attend?

Anyone involved with security operations, architecture, triage, or vulnerability/exposure management. Other titles may not be allowed to join.

Do I need to know anything about wine?

Not at all. If you can read a CVE, you can handle a tasting note.

What if I don’t drink?

You’re still welcome. Non-alcoholic option available.

Is this a sales pitch?

No. It’s a holiday thank-you to the TVM community. Hosted by Empirical Security.

Will it be recorded?

Not this time. Like a zero-day, you’ll have to be there to catch it.